The customer wants proof
A customer or tender asks about AI and security. Who has the answer?
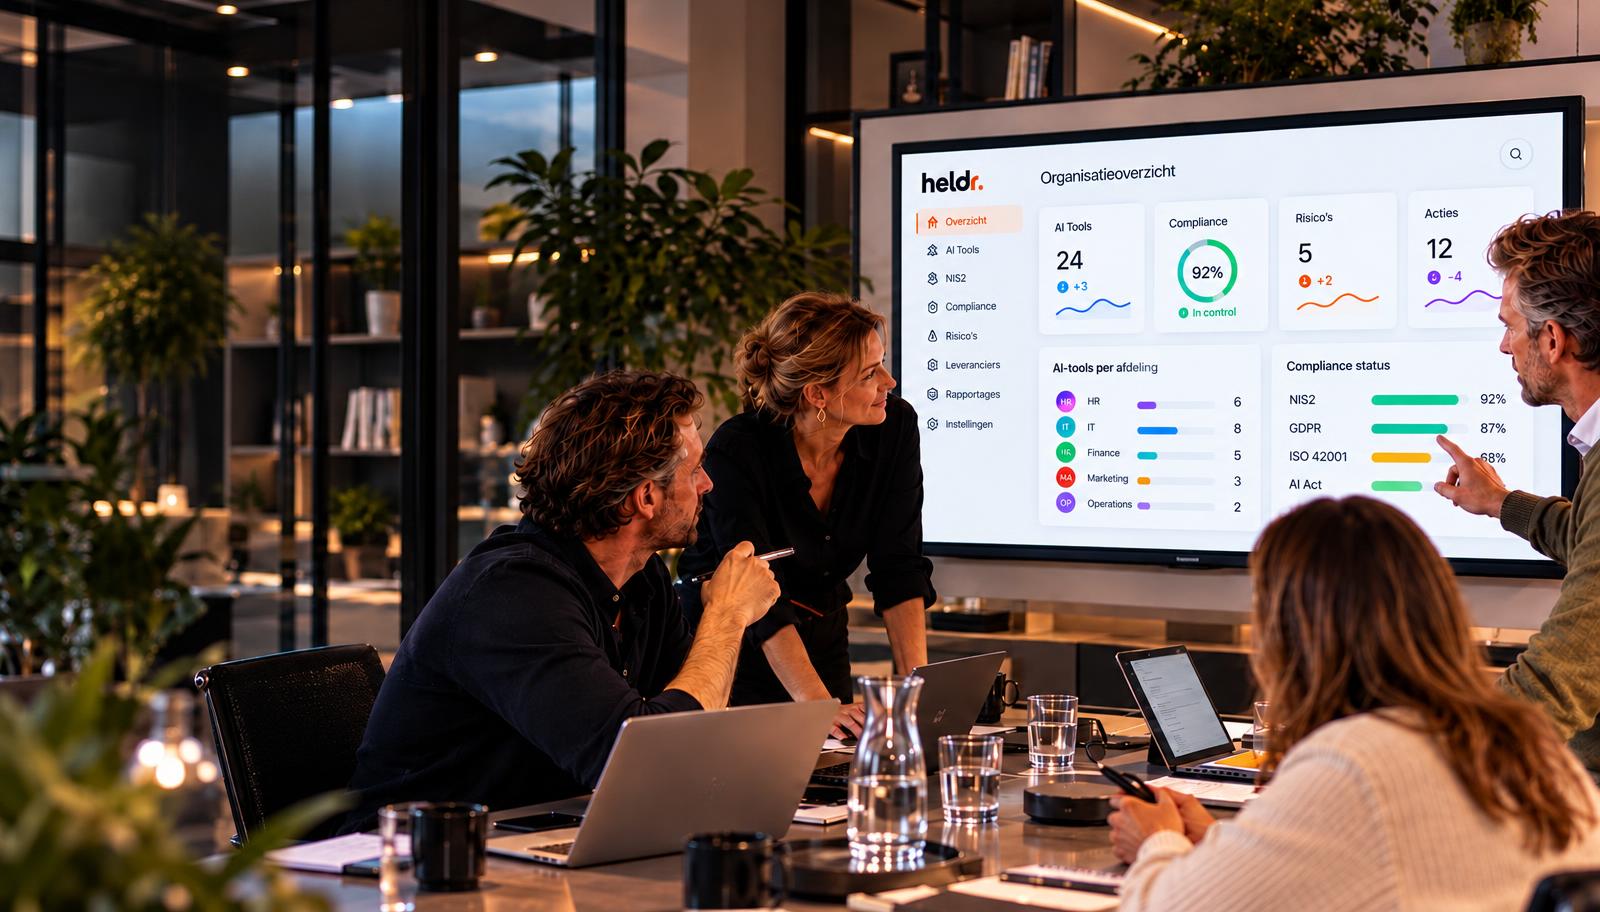
Visibility on AI. Without the chaos.
A customer or tender asks about AI and security. Who has the answer?
Your team uses AI tools. But which ones hold company data, and who keeps track?
NIS2, the Cyberbeveiligingswet. You hear the names, but what do they mean for your company?
Not for you if you already have a compliance department. You are probably fine.
| Option | What you get | What goes wrong |
|---|---|---|
| Consultant | A report | Outdated by next quarter. Next law, next invoice. |
| Compliance officer in house | A person | Too expensive for most SMBs, and the knowledge leaves with them. |
| Compliance software | A tool | Someone still has to fill it, read it and act on it. |
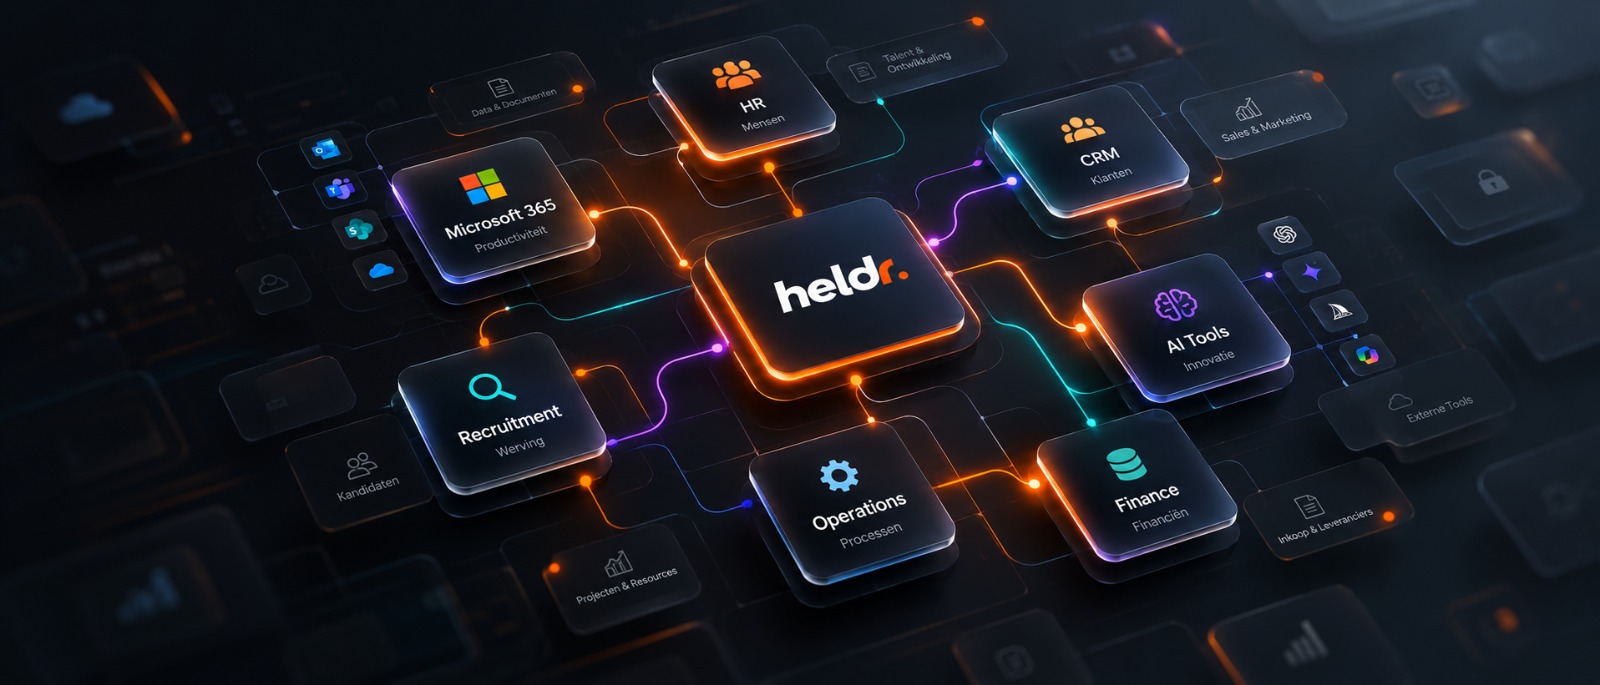
| heldr. | Platform and people | Always up to date. We do the heavy lifting, you stay in charge and know exactly who acts when something happens. Fixed monthly price. |
You can't outsource responsibility. The law asks you to own it. Heldr makes owning it doable.
We connect read only and map every AI tool (10 days)
What applies, what is missing, what to fix first
Heldr keeps watching and we handle the work, or you stop. No lock in.
1 in 5
Data breaches where shadow AI played a role. Average extra cost: $670,000.
IBM, 2025
63%
Breached organisations without an AI policy, or still writing one.
IBM, 2025
#1 in the EU
The Netherlands has the highest compliance burden of all member states, as a share of labour costs.
PwC, 2026
Checked 27 October 2026, 09:15 CET · last changed 2 August 2026